 Get in touch



DAC8 Compliance Software
From Day-1 Self-Certification to Regulatory Reporting Zero Remediation

Day-1 Readiness. Zero Remediation. From digital self-certification and real-time TIN validation to forensic due diligence, automated curing, account blocking compliance, and dual-track CRS 2.0 + CARF reporting — one OS, every DAC8 obligation, 27 EU member states.
Whatever You Operate The OS Is Configured for It
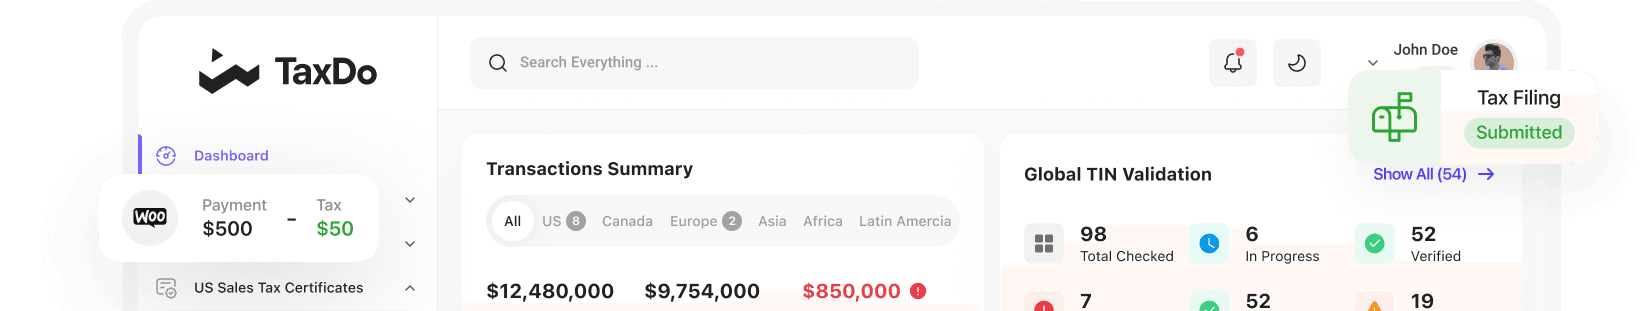
One OS for crypto exchanges and CASPs, fintechs and neo-banks, and payment and e-money platforms.

CRS 2.0 Track — Automated
TIN collection, self-certification validation, and Reasonableness Test on all reportable accounts — automated from Day 1. The OS tracks every reminder and self-certification deadline so your compliance team does not.

CARF Track — Automated
The OS brings CARF-specific self-certification and TIN validation into your existing onboarding. Exchanges, wallet providers, and CASPs under MiCA get the compliance infrastructure for crypto-asset user blocking and national penalty rules.

Full Due Diligence — Automated
Same indicia detection and curing workflows as banks. Cash-value products, controlling person look-through, and entity classification — all resolved inside the OS, per account, in real time.

Day-1 Infrastructure
Many have never operated under CRS-style due diligence. The OS provides the full self-certification, TIN validation, and reporting infrastructure DAC8 requires — deployed in weeks, not months.
Three Changes. Three Failure Points One Connects Them All

Identity Problem
Failure Point 1Validate every TIN against its issuing jurisdiction — in real time, across every country. Fail, and the reminder clock starts at Day 0.

Due Diligence Problem
Failure Point 2Every indicium must be detected and resolved — per account. Most tools collect first, review later. That gap becomes a remediation backlog growing with every account opened.
Due Diligence

Reporting Problem
Failure Point 3Dual-track CRS 2.0 + CARF filing across 27 member states. Different vendors mean different data layers.
The OS for Global Tax Identity & Regulatory Compliance Two Layers
Real-time identity validation and automated compliance intelligence — from the moment an account opens to the moment DAC8 reports are filed across 27 EU member states.
Global Tax Identity Infrastructure
DAC8 requires validated TINs for every account holder and controlling person across 27 EU member states — in real time, against official sources. The TaxDo identity layer delivers this at the point of onboarding, not months later during remediation.


Forensic Intelligence Engine
Sits on top of the identity infrastructure and runs automated due diligence across every account — detecting indicia, resolving discrepancies, and producing clearance records.
- Automated indicia detection across all account data at onboarding
- In-session auto-cure — 95%+ resolved before onboarding completes
- Immutable clearance record per account holder
- Mandatory Reasonableness Test — automated, audit-ready
- Account blocking compliance — full 2-reminder workflow of at least 60 days

From Onboarding to Reporting One OS. Every DAC8 Obligation. Covered

Forensic Due Diligence — At Onboarding
During self-certification, the Forensic Intelligence Engine detects indicia across dimensions, validates against official sources, and auto-cures discrepancies in real time. 95%+ of accounts resolved before onboarding completes. No manual review. No remediation backlog.

Pre-Existing Account Remediation
Bulk validation of your existing portfolio against DAC8 requirements. Gaps identified, discrepancies resolved, records upgraded to compliance standard. New and pre-existing account populations handled from one engine.

Digital Self-Certification Engine
Guided, jurisdiction-aware collection for individuals and entities. Automatic controlling person cascade for passive NFEs — identify, collect, validate, and report each natural person. eIDAS-compliant digital signature.

Dual-Track Regulatory Reporting
CRS 2.0 and CARF reports generated from one shared data layer. Local transposition variations handled per member state. Multi-jurisdiction output across 27 EU states in a single pass.
End-to-End DAC8 Lifecycle


Reduction in Manual DAC8 Due Diligence Cost.
Forensic due diligence runs inside self-certification — not after it. The 95% is not a target. It is a measured result.

Indicia Detected at Onboarding
Every indicium identified in real time, during self-certification — not weeks later by a review team.

Reasonableness Test Automated
Cross-checked against all information on file. Audit-ready from Day 1. No human intervention required.

Auto-Cured in the Same Session
Discrepancies resolved automatically before the account holder finishes onboarding. No manual queues.

Clearance Record per Account
Immutable audit trail. Every validation, every resolution, every decision — timestamped and retained.
The remediation teams, the spreadsheets, the year-end scramble — gone.
Not an additional cost. A replacement for the one you already carry.
Every Obligation. Automated
You know what DAC8 requires. Here is how the OS handles each obligation across 27 EU member states.
Self-Certification Collection
Digital collection at account opening: name, address, all jurisdictions of tax residence, TIN per reportable jurisdiction, entity type, and controlling persons. Paper/PDF forms are non-compliant under CRS 2.0.
TIN Validation & Reasonableness Test
Validate every TIN against the issuing jurisdiction's format and issuance rules. Cross-check self-certifications against all information on file. Cannot accept self-certifications known or suspected to be incorrect.
Indicia Detection & Due Diligence
Systematic detection of discrepancies between declared tax residence and observable data. Each indicium investigated, documented, and cured or escalated. Burden of proof on the reporting entity.
Two Account Populations, One Deadline
New accounts require due diligence from Day 1. Pre-existing accounts must be reviewed, remediated, and brought to DAC8 standard. Both populations face the same national penalty rules.
Entity Classification & Controlling Persons
Classify every entity as FI, active NFE, or passive NFE. Passive NFEs trigger mandatory controlling person look-through — identify each natural person, collect their self-certification, validate their TIN, and report separately.
Two Reminders, At Least 60 Days
Two formal reminders and at least 60 days from the first request, all documented. Every reminder, response, and deadline tracked and logged with an immutable audit trail. No manual deadline tracking.
Mandatory Account Blocking
After two reminders and at least 60 days: if a crypto-asset user has not provided a valid self-certification, the provider must block them from reportable transactions. No exceptions. No discretion.
CRS 2.0 + CARF Reporting
File under both CRS 2.0 (financial accounts) and CARF (crypto transactions) where applicable. Each of 27 member states may have local format and submission variations — all handled by the OS.
DAC8 Has Been Enforced Since 1 January 2026 Each Gap Can Be a Separate Infringement
Penalties Set by Each Member State
DAC8 requires national penalties to be effective, proportionate and dissuasive. Each missing TIN, unvalidated self-certification, or unreported account can be a separate infringement, so liability compounds across your entire portfolio.
Supervisory Attention on Systemic Gaps
Systemic non-compliance under CRS 2.0 or CARF tracks draws supervisory attention, and each member state decides how severely to penalise it.
Loss of EU Registration
A non-EU crypto-asset operator that does not report after two reminders can have its registration in the EU revoked and, as a last resort, be prevented from operating in the Union (DAC8, Annex VI, Section V.F).
Blocking Disrupts Revenue
Blocking = locked funds, customer attrition, support escalation, potential litigation. Account blocking is a customer experience crisis, not just a compliance event.
Regulatory Scrutiny
Each member state supervises DAC8 compliance and sets its own penalties (Art. 25a DAC, as amended by DAC8), so the same gap can be treated differently in every market you serve.
What Most Get Wrong
Paper self-certifications: non-compliant. Manual remediation: non-compliant. Year-end review cycles: too late. The reminder clock starts at the first request, not at your annual review.
Enforced Across the EU Since 1 January 2026


27 EU Member States Under DAC8
DAC8 applies uniformly across all 27 EU member states. Every financial institution, crypto exchange, and CASP operating in these jurisdictions must comply — with national transposition complete by 31 December 2025.
Western Europe9


Central & Eastern Europe7


Southern Europe6


Northern Europe5


Source: Council Directive (EU) 2023/2226 National transposition deadline: 31 December 2025. First reporting period: January–September 2027.
Questions from Compliance Teams
We will respond to you at any time. Just use our help center or contact us.
DAC8 is Council Directive (EU) 2023/2226, the eighth amendment to the EU Directive on Administrative Cooperation. It brings crypto-assets into the EU’s automatic exchange of tax information by implementing CARF into EU law, and applies across all 27 member states from 1 January 2026. Every crypto-asset service provider under MiCA (exchanges, custodial wallet providers and platforms facilitating buys, sells, exchanges and transfers) must collect self-certifications, validate TINs and report. A crypto-asset user who still has not self-certified must be blocked from reportable transactions, after two reminders and at least 60 days. Penalties are set by each member state.
Yes. DAC8 implements CARF into EU law. Every crypto-asset service provider under MiCA (exchanges, custodial wallet providers, platforms facilitating buys, sells, exchanges, and transfers) must collect self-certifications, validate TINs, and report under the CARF track. A crypto-asset user who still has not self-certified must be blocked from reportable transactions, after two reminders and at least 60 days. Penalties are set by each member state.
If a crypto-asset user fails to provide a valid self-certification after two formal reminders, and at least 60 days after the first request, the crypto-asset service provider must block them from reportable transactions. Not discretionary. Blocked users cannot make reportable transactions until they provide the required information.
Penalties are set by each member state; DAC8 requires them to be effective, proportionate and dissuasive. Each missing TIN or unreported account can be a separate infringement under national rules.
DAC8 operates on two tracks: CRS 2.0 covers financial accounts and balances (banks, custodians, insurers). CARF covers crypto-asset transactions (exchanges, wallet providers, CASPs). A crypto exchange with fiat accounts may fall under both. Shared due diligence, divergent reporting.
Enforcement began 1 January 2026. First reporting period: January–September 2027 for the 2026 year. Institutions must collect compliant self-certifications from Day 1 of 2026.
Mandatory under CRS 2.0 and DAC8. Cross-checks the self-certification against all information held by the institution — across multiple data dimensions and indicia categories. Institutions cannot accept self-certifications that are known or reasonably suspected to be incorrect or unreliable.
No. Paper and PDF self-certifications cannot support real-time TIN validation (mandatory under CRS 2.0), cannot trigger automated cure workflows, and cannot produce structured audit trails. They cannot operationally support the real-time validation and reasonableness checks DAC8 requires.
Yes. Same self-certification, TIN validation, Reasonableness Test, and reporting requirements as established banks.

DAC8 Is One Engine Inside the OS. Everything Else Connects.

Global Tax Identity
The identity foundation that powers every framework. TIN validation, business registry verification, and entity intelligence across 210+ countries. Layer 1 of the OS.


Regulatory Compliance Intelligence & Reporting
CRS 2.0, CARF, DAC8, DAC7, FATCA — same OS, same identity layer, regime-specific output.

Global Indirect Tax
VAT/GST determination, US Sales Tax, and cross-border indirect tax compliance — connected to the same entity and identity data that drives transparency reporting.
Ready to Replace Separate Tools with One OS?
From self-certification to dual-track reporting — every DAC8 obligation automated through real-time TIN validation, forensic due diligence, automated curing, and account blocking compliance. Deployed in weeks across 27 EU member states.