Get in touch
Sources last verified: 28 October 2026
Official sources cited at the end of this page.
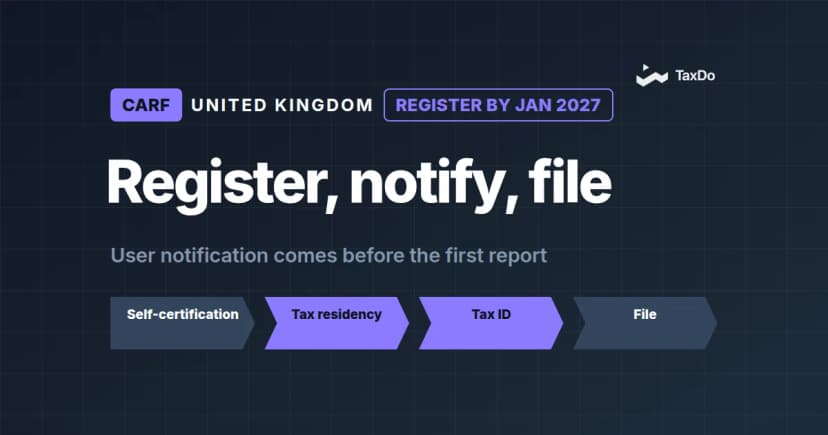
Four dates now define the UK’s crypto reporting year. By 31 December 2026, a UK reporting cryptoasset service provider must hold a valid self-certification for every user it already served before 2026; by 31 January 2027, it must tell its users that their 2026 data will go to HM Revenue & Customs (HMRC); by 31 May 2027, it files the first annual report under the OECD’s Crypto-Asset Reporting Framework as applied by SI 2025/744; and every calendar year since 1 January 2026 has been a reporting year. Under section 275 of the Finance Act 2026, the report also covers UK-resident users from the 2026 reporting year onward.
The obligation the regulations put first is due diligence on every user, and it is priced per head: up to £300 for each reportable user or reportable person without a valid self-certification. HMRC expects a new user’s self-certification before the first transaction, so a provider that onboarded users in 2026 without one is already exposed.
The criminal law sits behind it. Under the Criminal Finances Act 2017, a firm whose staff, agents or others performing services for it criminally facilitate tax evasion commits an offence unless it had reasonable prevention procedures, or could not reasonably be expected to have any, and weak onboarding controls are hard to defend as reasonable.
There are two ways to meet the UK rules. One runs a campaign to collect self-certifications from existing users before the 31 December 2026 deadline and reconciles them against KYC data. The other completes and tests each one inside onboarding, before the first trade, which is when HMRC expects it for every new user. Only the second produces that record as the user signs up.
01 · UK CARF at a Glance
| Point | Position as at 28 October 2026 |
| Legal basis | Reporting Cryptoasset Service Providers (Due Diligence and Reporting Requirements) Regulations 2025, SI 2025/744; Finance Act 2026, s. 275 |
| Authority | HM Revenue & Customs (HMRC) |
| In force | 1 January 2026 (reg. 1) |
| Who reports | UK reporting cryptoasset service providers: tax residence, incorporation, management or a regular place of business in the UK, or a UK branch (reg. 3) |
| Who is reported | Users resident in reportable jurisdictions and, from the 2026 reporting year, users resident in the UK (Finance Act 2026, s. 275) |
| Existing users | Valid self-certification by 31 December 2026 for users onboarded before 2026 (HMRC guidance) |
| Notify users | By 31 January after the first reporting year: 31 January 2027 (reg. 8) |
| Register | Later of 31 May 2027 and 31 January after the first year in scope (reg. 10); HMRC’s guidance asks for 31 January 2027 |
| Report | By 31 May after each calendar year, electronically in the form HMRC directs (regs. 6, 7); an XML file under HMRC’s guidance |
| Records | Five years from the day after the end of the calendar year they relate to (reg. 4) |
| Penalties | Up to £300 per reportable user or person without a valid self-certification; late report up to £5,000, then up to £600 a day after assessment (regs. 11, 14) |
| First exchange | 2027 |
Our regulatory compliance engine builds the UK due diligence record as each user signs up. It collects and checks the self-certification, runs the TIN, reasonableness and other required due diligence checks, resolves indicia automatically instead of by your compliance team, and prepares the validated report, with zero remediation.
02 · Critical Timeline: The 2026 Reporting Year
The regulations came into force on 1 January 2026 and apply “the rules”: the OECD’s CARF and commentary, published in 2022 and amended in 2023, as modified from time to time (reg. 2(1)). Reporting runs by calendar year (reg. 2(4)(a)), and HMRC publishes by notice the lists of reportable and partner jurisdictions (reg. 2(4)(c), (d)).
| Date | What falls due | Provision |
| 1 January 2026 | Due diligence on users; transactions start counting | reg. 1, reg. 4 |
| 31 December 2026 | Valid self-certification for every user onboarded before 2026 | HMRC guidance |
| 31 January 2027 | Notify each user whose data will be reported | reg. 8 |
| 31 May 2027 | First report, for 2026; registration under reg. 10 (HMRC’s guidance: 31 January 2027) | regs. 6, 10 |
| 31 May 2027 | Section I(H) notification for 2026, for a provider with an equal nexus that reports in a partner jurisdiction | reg. 3(2) |
| 31 May each year | Annual report | reg. 6 |
On registration the sources differ. The regulations set the later of 31 May 2027 and 31 January after the first year in scope, which for a provider in scope in 2026 is 31 May 2027; HMRC’s guidance page asks providers to register by 31 January 2027, through an online service it describes as not yet live. Registering by the earlier date satisfies both. HMRC’s guidance also adds two expectations the regulations do not state: the 31 December 2026 deadline for existing users and a stop on transacting for a user without a valid self-certification (section 04).
03 · Who Is in Scope? (UK Perimeter)
UK-based RCASPs
A reporting cryptoasset service provider effectuates exchange transactions for users as a business, including by making a trading platform available. It is UK-based if it is tax resident, incorporated or managed in the UK, or has a regular place of business here, and transactions through a UK branch are reported here too (reg. 3; HMRC guidance). A provider based in several countries reports in the one ranked highest, with tax residence first, and can notify HMRC under Section I(H) where it has an equal nexus in a partner jurisdiction and reports there (reg. 3(2)).
EMIs and e-money
E-money falls on the CRS side. Specified electronic money products and central bank digital currencies are excluded from CARF’s relevant crypto-assets, and an e-money institution holding them for customers is a depository institution under the amended International Tax Compliance Regulations 2015 instead, reporting only e-money accounts whose 90-day rolling average balance exceeds USD 10,000.
Traditional banks and wealth managers
Financial institutions report under the CRS, amended by SI 2025/740: registration and a revised penalty table took effect on 16 July 2025, and the reporting changes, including new data fields and e-money accounts, from 1 January 2026. Gross proceeds already reported under the CARF need not be reported again under the CRS unless the institution elects (SI 2015/878, reg. 7A). Our UK CRS 2.0 article covers that side in full.
04 · Day 1 Roadmap for UK Compliance
Collect and test the self-certification
The provider applies the due diligence in Section III of the rules and keeps a record of the steps taken and the information collected (reg. 4). Users and controlling persons asked for a self-certification must provide one that meets the rules’ validity requirements (reg. 5); an entity’s controlling persons are identified only where it is neither an excluded person nor an active entity.
Users onboarded before 2026
SI 2025/744 sets no date of its own: the OECD rules it applies allow twelve months from the effective date. HMRC’s guidance fixes it: a user with a relationship in place on 1 January 2026 must have a valid self-certification by 31 December 2026, and HMRC advises obtaining it before continuing to transact for that user.
No blocking rule in the text, but HMRC expects a stop
Unlike the EU’s DAC8, SI 2025/744 contains no rule requiring a provider to block a user who does not self-certify. HMRC’s guidance goes further than the text: where a valid self-certification is not obtained within the time limits, a provider should stop effectuating relevant transactions for that user. The regulations add penalties: up to £300 on a provider for each reportable user or reportable person it failed to obtain a valid self-certification for (reg. 11(2)), and up to £300 on a user whose failure to provide one is deliberate or careless (reg. 13).
A Manchester broker’s exposure
Take a fictional crypto broker in Manchester that onboarded 4,000 users in 2026, 250 of them without a valid self-certification. If all 250 are reportable users, its maximum exposure under regulation 11(2) is 250 × £300, £75,000, with HMRC setting the amount it considers appropriate within that limit (reg. 22) and a reasonable excuse removing it; if its report is also late, regulation 14 adds up to £5,000 and up to £600 a day once a penalty has been assessed.
05 · Reporting, Records and Penalties
Reports go to HMRC electronically by 31 May, in the form HMRC directs, and a report not made that way is treated as not made (regs. 6 and 7). HMRC’s guidance says the report is an XML file of up to 250MB, filed through an online service that was not yet live, and that no report is needed where there is nothing to report (HMRC, reporting cryptoasset user and transaction data).
| Failure | Maximum penalty | Reg. |
| Due diligence not applied | £100 per reportable user or person; £300 where the failure is a missing valid self-certification | 11 |
| Records not kept | £5,000 per calendar year | 12 |
| User fails to self-certify (deliberate or careless) | £300, on the user | 13 |
| Late report | £5,000, then up to £600 a day after assessment | 14 |
| Inaccurate or incomplete report | £100 per user, if deliberate, careless, or found later and HMRC not told | 15 |
| Users not notified | £100 per person, then up to £100 a day | 16 |
| Failure to register | £1,000, then up to £300 a day | 18 |
A reasonable excuse removes liability, but neither a lack of funds nor reliance on another person counts (reg. 20). Regulation 26 disregards arrangements one of whose main purposes is to avoid an obligation under SI 2025/744.
06 · UK-Resident Users and the Finance Act 2026
Section 275 of the Finance Act 2026 extends the report to users resident in the UK for income tax or corporation tax purposes, and to entities with UK-resident controlling persons, as if they were reportable users. Those users must be notified that their data goes to HMRC, though not that it may be sent abroad, and a provider cannot use the Section I(H) partner-jurisdiction relief for this domestic reporting.
Every user therefore needs a residence determination, and every UK-resident user’s transactions now go to HMRC.
07 · The Corporate Criminal Offence: Why “Wait and See” Is a Risk
Section 45 of the Criminal Finances Act 2017 makes a company or partnership guilty of an offence when a person associated with it, such as an employee, an agent or another person performing services for it, commits a UK tax evasion facilitation offence while acting in that capacity. It is a defence to prove that the body had prevention procedures that were reasonable in the circumstances, or that it was not reasonable to expect it to have any. Section 46 extends the offence to facilitating foreign tax evasion where the body is UK-incorporated or formed, carries on business in the UK, or part of the conduct takes place here, and the conduct is criminal under both the foreign law and UK law. The penalty is a fine (s. 45(8)).
CARF reporting is not itself a CCO duty, and a failed self-certification is not a criminal offence. The link is evidential: the government’s guidance sets six principles for reasonable prevention procedures, among them risk assessment, due diligence and monitoring, and a provider that knowingly onboards users without checking their declared residence will struggle to show the procedures it had were reasonable.
08 · Two Ways to Meet the UK Rules
By campaign before 31 December 2026
For users already on the books, a provider can collect self-certifications by campaign, chase the gaps and reconcile them against KYC data before the 31 December 2026 deadline. It works for a small book. The cost is the regulation 11 exposure on every reportable user still missing at the deadline, and the transactions HMRC advises holding back until the self-certification is in, with a penalty position if they continue after 31 December 2026. For new users the campaign route is not available: the self-certification belongs at onboarding.
Inside onboarding, step by step
TaxDo runs CARF due diligence inside onboarding, from the first user self-certification to the validated report, in five steps.
Step 1 · Collect the self-certification. Guided, one question at a time, for individuals and entities, with a digital signature; controlling persons are collected in the same flow where the entity requires them.
Step 2 · Validate the identity. Every TIN is checked in real time against official sources in 130+ countries, and the business against registries in 120+.
Step 3 · Run forensic due diligence with Verify+. Our Verify+ forensic engine runs 20+ checks on an individual and 30+ tax-native checks across eight areas on an entity, testing each self-certification against the data already held and classifying each transaction by reportable type.
Step 4 · Cure the gaps, without the compliance team:
4a · New users. Discrepancies are resolved in the same session, before the first trade.
4b · Existing users. One click starts remediation for the pre-2026 book through a link in your own brand, with every answer checked by Verify+ and each case closed by a signed self-certification and an audit-ready certificate.
Step 5 · Report, and keep the evidence. Schema-validated CARF XML from one data layer, prepared and validated for your platform to submit. Our team can also submit it on your behalf on request, as an additional service. Every user keeps an immutable clearance record.
From Day-1 self-certification to CARF reporting, with zero remediation. Every user is cleared at onboarding.
Our CARF compliance software · Crypto exchanges and CASPs
Where this sits, and what it does not touch
It runs beside the KYC process money-laundering regulation already requires, not in place of it. The reporting obligation, and the responsibility for what is reported, stays with the provider, including where TaxDo submits the report on its behalf at its request. TaxDo runs the due diligence and prepares and validates the report.
09 · Recent Changes and What’s Next
24 June 2025
The CARF regulations (SI 2025/744) and the CRS amendments (SI 2025/740) are made.
1 January 2026
CARF due diligence and the first reporting year begin.
18 March 2026
Finance Act 2026 receives Royal Assent; s. 275 extends reporting to UK-resident users from the 2026 reporting year.
31 December 2026
Valid self-certifications due for users onboarded before 2026, under HMRC’s guidance.
31 January 2027
User notifications due; HMRC’s guidance also asks for registration by this date.
31 May 2027
First CARF report; the UK is listed for first exchanges in 2027 (OECD list of 14 September 2026). In the EU, DAC8 has applied since 1 January 2026, and a provider within its scope reports its EU-resident users under it; see our DAC8 compliance software. Neighbouring rules: our France CARF and Finland CARF articles.
10 · Related Reading
Framework articles: CARF and crypto tax transparency · CRS 2.0 compliance guide for banks · Self-certification under CRS 2.0, DAC8 and CARF · UK CRS 2.0 · France CARF · Finland CARF
Product: Regulatory compliance engine · CRS compliance software · Day 1 onboarding validation