Get in touch
Sources last verified: 28 October 2026
Official sources cited at the end of this page.
A Vienna crypto broker licensed under MiCA opens an account for a new customer in October 2026. Under Austria’s Krypto-Meldepflichtgesetz (Krypto-MPfG), it may establish that relationship only once it holds a valid self-certification, and the customer’s 2026 transactions go to the tax authorities by 31 July 2027 even if he is resident in Austria. The law, in force since 1 January 2026, applies the EU’s DAC8 and the OECD’s Crypto-Asset Reporting Framework.
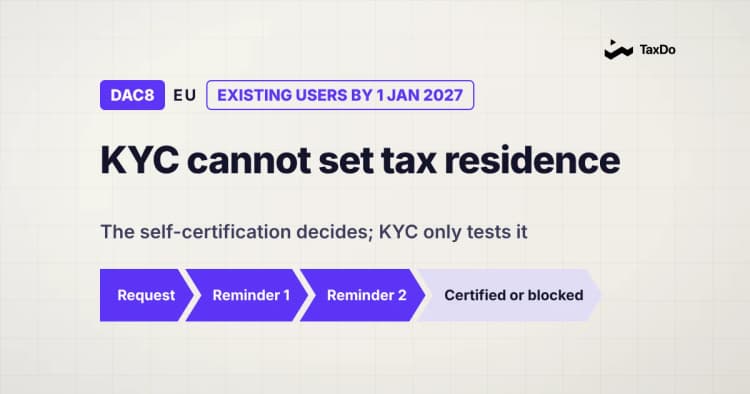
The broker’s customers from before 2026 are on a different clock: each must have given a self-certification by 1 January 2027. A customer who still has not provided the missing information after a written request and two reminders must be stopped from carrying out reportable transactions, no earlier than 60 days after the first request.
The penalties are set in the Krypto-MPfG itself: up to €200,000 for an intentional reporting or registration breach, and up to €20,000 for an intentional due diligence breach.
There are two ways to meet the Austrian rules. One chases the existing book before 1 January 2027 and runs the reminder procedure for every gap. The other completes and checks the self-certification at onboarding, as the law already requires for new users, and applies the same flow to the existing book. Only the second keeps the blocking rule a rare event.
01 · Austria CARF at a Glance
| Point | Position as at 28 October 2026 |
| Law | Krypto-Meldepflichtgesetz (Krypto-MPfG), Article 1 of the Betrugsbekämpfungsgesetz 2025 Teil Daten, BGBl. I Nr. 96/2025 |
| Regulation | Krypto-MPfG-Durchführungsverordnung, BGBl. II Nr. 331/2025 |
| In force | 1 January 2026 (§ 46) |
| Authority | Finanzamt für Großbetriebe (§ 3) |
| Who reports | A provider authorised in Austria under MiCA (Art. 63), or entitled to provide crypto-asset services here after a MiCA Art. 60 notification; otherwise one tax resident, incorporated, managed or with a branch or regular place of business in Austria, in that order (§ 15) |
| Who is reported | Users resident in participating states, which include Austria |
| New users | Valid self-certification before the relationship is established (§ 28(3)) |
| Existing users | Relationship before 1 January 2026; self-certification by 1 January 2027 (§ 28(2), § 30(3)) |
| Missing information | Request, two reminders, then transactions blocked no earlier than 60 days after the request (§ 38) |
| Report | Calendar year, by 31 July of the following year (§ 19(2)); first for 2026 by 31 July 2027 |
| Records | Ten years after the end of the reporting period (§ 39) |
| Penalties | Up to €200,000 reporting or registration; up to €20,000 due diligence (§§ 40 to 42) |
Our regulatory compliance engine builds the Krypto-MPfG due diligence record as each user signs up. It collects and checks the self-certification, runs the TIN, reasonableness and other required due diligence checks, resolves discrepancies automatically instead of by your compliance team, and prepares the validated report, with zero remediation.
02 · The Law and Its Place in DAC8 and CARF
The Krypto-MPfG is Article 1 of the Betrugsbekämpfungsgesetz 2025 Teil Daten, published as BGBl. I Nr. 96/2025. The Finance Committee adopted the government bill unchanged (332 d.B.), the Nationalrat passed it on 10 December 2025 and the Bundesrat raised no objection on 18 December 2025. It transposes Directive (EU) 2023/2226 (DAC8) and also governs exchanges with third countries under the OECD’s Crypto-Asset Reporting Framework, approved by the OECD Committee on Fiscal Affairs over 2022 and 2023 and published with its Commentary on 8 June 2023.
Austria signed the CARF multilateral agreement on 21 November 2024 and is listed among the 46 jurisdictions committed to first exchanges by 2027 (Global Forum, 14 September 2026). The same law amends the Gemeinsamer Meldestandard-Gesetz for the amended CRS; our Austria CRS 2.0 article covers that side.
03 · Regulatory Compliance for Crypto-Asset Service Providers in Austria
Who reports
A reporting crypto-asset service provider is subject to the Austrian duties first if it is authorised in Austria under Article 63 of MiCA, Regulation (EU) 2023/1114, or entitled to provide crypto-asset services in Austria following a notification under Article 60 (§ 15(1) Z 1). If it is not, the law applies in a fixed order: tax residence in Austria; incorporation or organisation under Austrian law with legal personality or a tax filing obligation here; management from Austria; or a branch, or for an individual a regular place of business, in Austria (§ 15(1) Z 2). Transactions through an Austrian branch are covered too (§ 15(2)). A provider whose Austrian link under § 15(1) Z 2 ranks no higher than its link to another member state or qualifying third country, and which reports there, is exempt if it notifies the Finanzamt by 1 October of the following year with proof of that reporting (§§ 16 and 17).
Registration
A crypto-asset operator without a MiCA authorisation whose reporting falls to Austria under § 15(1) Z 2, and which is not exempt, must register by 31 December 2026, or within one month of starting if it starts after that date (§ 22(1)). It receives an individual identification number (§ 24), and an operator that fails to report after two reminders has its registration revoked (§ 25). The Durchführungsverordnung sets the procedure: registration through the Ministry of Finance’s IIN-CAO web form, and exemption notifications, changes and reports through FinanzOnline.
Who is reported
Only information about participating states is reportable (§ 19(3)), and every EU member state, Austria included, is a participating state (§ 14(1) Z 1). Austrian residents are therefore reported, a difference from the CRS rules, under which Austria is not itself a participating state (§ 91 Z 1 Gemeinsamer Meldestandard-Gesetz). Our DAC8 compliance software reports Austrian and other EU residents from the same data.
04 · Due Diligence: Self-Certification and the Blocking Rule
For a new user, the relationship may be established only once a valid self-certification is in hand (§ 28(3)). For an existing user, one whose business relationship began before 1 January 2026 (§ 7(5)), the provider must obtain it by 1 January 2027 (§ 28(2); § 30(3) for entities). Entities give their controlling persons where required (§§ 31 and 37), and a change of circumstances calls for a new self-certification or a reasonable explanation (§§ 29 and 32).
Section 38 sets out what happens when information is missing. The provider asks the user in writing to supply it by no later than three months after the end of the reporting period, so by 31 March for the previous year (§ 38(1)). If the user misses that deadline, the provider sends two written reminders at least seven days apart (§ 38(2)). If the user has not complied within seven days of the second reminder, the provider must prevent the user from carrying out reportable transactions, no earlier than 60 days after the original request, for as long as the information is missing (§ 38(3)). The explanatory notes count the 60 days from the second reminder; the statute counts from the original request.
A Graz broker’s 2027 calendar
Take a fictional broker in Graz with an existing customer who has given no self-certification by 1 January 2027. It requests the information on 15 February 2027, asking for it by 31 March 2027. The customer misses that date, so the broker sends reminders on 1 April and 8 April. If the customer has not responded by 15 April, the broker must block reportable transactions, from 16 April 2027 at the earliest, the 60th day after the request. Every customer documented at onboarding is one fewer case in that sequence.
05 · Reporting, Notification and Records
The reporting period is the calendar year (§ 19(1)), and the report for each year is due by 31 July of the following year (§ 19(2)), so the first, for 2026, is due by 31 July 2027. The Federal Minister of Finance passes the information to other competent authorities within nine months of the year end (§ 21). Each user must be told before the first report that their information is reportable, in time to exercise their data-protection rights (§ 20).
Reports and notifications go electronically through FinanzOnline under the Durchführungsverordnung. Documentation of the reporting and due diligence steps is kept for ten years after the end of the reporting period and then deleted (§ 39), the maximum DAC8 allows (five to ten years), against a five-year minimum in the OECD model.
What a report contains
The report follows the DAC8 and CARF structure. For each reportable user it gives the user’s identification, residence and TIN, and for each type of crypto-asset annual aggregates: amounts paid and received in exchanges against fiat currency, the fair market value of exchanges against other crypto-assets, reportable retail payment transactions, other transfers to and by the user, and transfers to wallet addresses not known to belong to a provider or financial institution. The report does not list individual trades, but the provider must capture and store the information for every customer and every transaction (§ 20(1)), so each aggregate has to be traceable to the transactions behind it, which is where most data-quality work sits.
Foreign providers and the Austrian nexus
Section 15, with the exemptions in §§ 16 and 17, decides whether a provider reports to Austria. A provider authorised under MiCA in Austria, or entitled to serve here after an Article 60 notification, reports here, whatever its tax residence; one authorised in another member state reports there, even for Austrian customers, unless the transactions run through an Austrian branch, which reports here (§ 15(2)); Austria receives the rest by exchange. A provider with no MiCA authorisation is caught only if it has an Austrian link under § 15(1) Z 2, such as tax residence, management or a place of business here; it must then register under § 22 unless it is exempt under §§ 16 and 17, because its link elsewhere ranks equal or higher, it reports there and it has notified the Finanzamt. For an international group, the first task is therefore to map each entity’s nexus under § 15 before deciding where self-certifications and reports are produced.
06 · Penalties
| Breach | Intentional | Grossly negligent | § |
| Report not made, late, incomplete or incorrect | Up to €200,000 | Up to €100,000 | 40 |
| Registration duties | Up to €200,000 | Up to €100,000 | 41 |
| Due diligence duties | Up to €20,000 | Up to €10,000 | 42 |
Reporting and registration breaches are finance offences (Finanzvergehen) and due diligence breaches finance misdemeanours (Finanzordnungswidrigkeiten); the courts never deal with the offences under §§ 40 and 41, which stay with the finance criminal authorities (§ 43).
07 · Operational Workflow and Compliance Tools
TaxDo runs Krypto-MPfG due diligence inside onboarding, in five steps.
Step 1 · Collect the self-certification. Guided, one question at a time, for individuals and entities, with a digital signature.
Step 2 · Validate the identity. Every TIN is checked in real time against official sources in 130+ countries, and the business against registries in 120+.
Step 3 · Run forensic due diligence with Verify+. Our Verify+ forensic engine runs 20+ checks on an individual and 30+ tax-native checks across eight areas on an entity, testing each self-certification against the data already held.
Step 4 · Cure the gaps, without the compliance team:
4a · New users. Discrepancies are resolved in the same session, before the relationship is established.
4b · Existing users. One click starts remediation for the pre-2026 book through a branded link, each case closed by a signed self-certification and an audit-ready certificate.
Step 5 · Report, and keep the evidence. Schema-validated XML from one data layer, prepared and validated for you, or your professional representative, to submit through FinanzOnline.
From Day-1 self-certification to the July report, with zero remediation. Every user is cleared at onboarding.
Our DAC8 compliance software · Crypto exchanges and CASPs
It runs beside the anti-money-laundering procedures a provider already applies, not in place of them. The reporting obligation, and the responsibility for what is reported, stays with the provider.
08 · Looking Ahead
The dates to plan around are 31 December 2026 for registration where it applies, 1 January 2027 for existing users’ self-certifications and 31 July 2027 for the first report. Other member states apply DAC8 from the same date with their own procedures; our DAC8 compliance guide sets out the common rules and our CARF compliance software covers exchanges with third countries.
09 · Related Reading
Framework articles: CARF and crypto tax transparency · DAC8 compliance guide · Self-certification under CRS 2.0, DAC8 and CARF · Austria CRS 2.0 · Greece CRS 2.0
Product: Regulatory compliance engine · CRS compliance software · Day 1 onboarding validation